HTML validation serves to ensure platform security by only processing and saving HTML formattings in the database that are classified as secure. All other HTML formattings and other codes and scripts are filtered beforehand (including enclosed content) and thus automatically removed from the text entered.
By default, HTML validation is activated for the platform.
Permitted HTML Formats
The following HTML formats are classified as secure and are thus not automatically removed if HTML validation is activated for the platform:
-
Permitted HTML tags: a, b, blockquote, br, caption, cite, code, col, colgroup, dd, dl, dt, em, h1, h2, h3, h4, h5, h6, hr, i, img, li, ol, p, pre, q, small, strike, strong, sub, sup, table, tbody, td, tfoot, th, thead, tr, u, ul
-
HTML tags, for which the "style" attribute is permitted: p, li, h1, h2, h3, h4, h5, h6, img, span
-
HTML tags, for which the "id" attribute is permitted: span
-
HTML tags, for which the "target" attribute is permitted: a
The following characters are also removed or replaced if HTML validation is activated for the platform:
-
The characters "<", ">" and "\" are replaced by the HTML special characters "<", ">" and "\", if they are not found as part of unauthorised HTML tags.
-
Characters with Unicode values 0-32, 5760, 6158 8192-8198, 8200-8202, 8232, 8287, 12288 are removed.
Components, for which HTML Sanitisation Applies
All text entry fields that have an HTML editor are subject to HTML sanitisation. HTML sanitisation is also applied for registration message texts and meta tags with entry fields.
Bypass Sanitisation
Administrators can skip the HTML sanitisation of system texts and enrolment messages (see screenshot below). This allows HTML in system texts to be displayed as intended after saving the system text using the backend without being altered by sanitisation. This improves ease of use for administrators but decreases the security level.
This setting disables a security safeguard. Use it only when required and after carefully reviewing the affected HTML content.
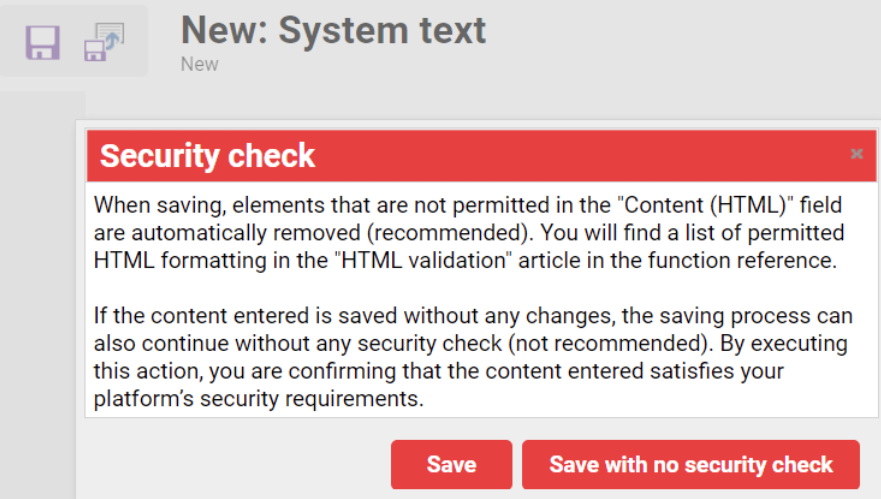
In the security configuration, the option “Skip sanitising system texts with confirmation” and the option “Bypass“ for enrolment messages need to be selected to use the skip functionality.